Risk Management and Gap Analysis
risk profiles and framework gap assessments on NIST SP 800-53
Know where you stand against every framework you answer to, and which control closes the most of the gap.
Risk and compliance teams answer to several frameworks at once, such as NIS2, DORA, PCI DSS and HIPAA, and assess each in its own spreadsheet. Scores rest on self-assessment alone, nobody can say which control would satisfy the most requirements, and the board sees a percentage with no plan behind it.
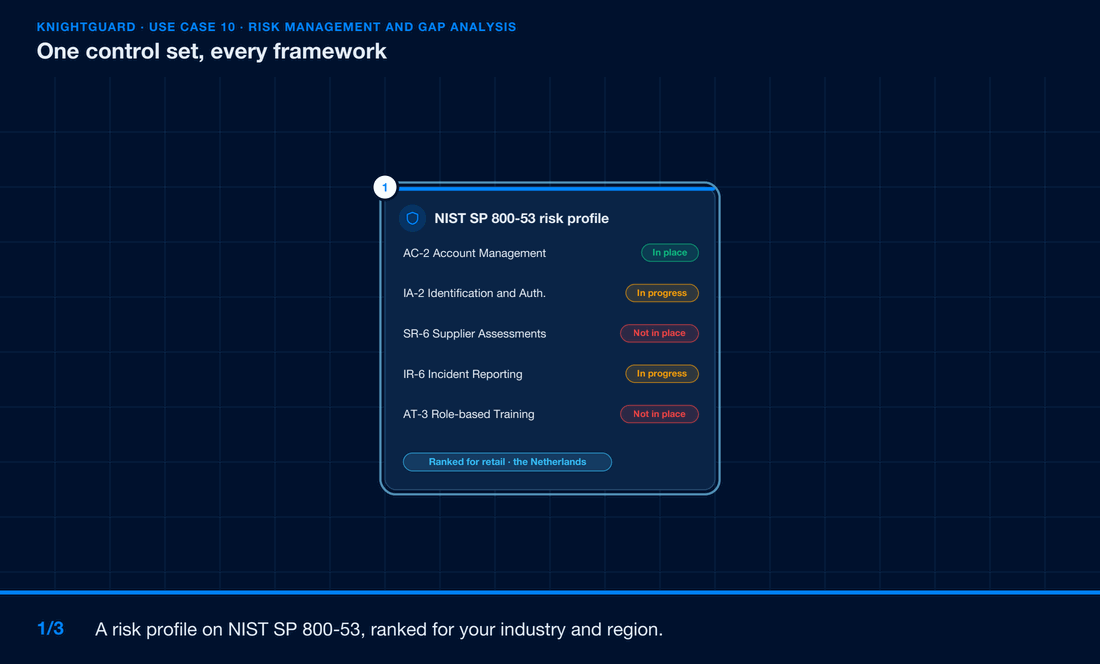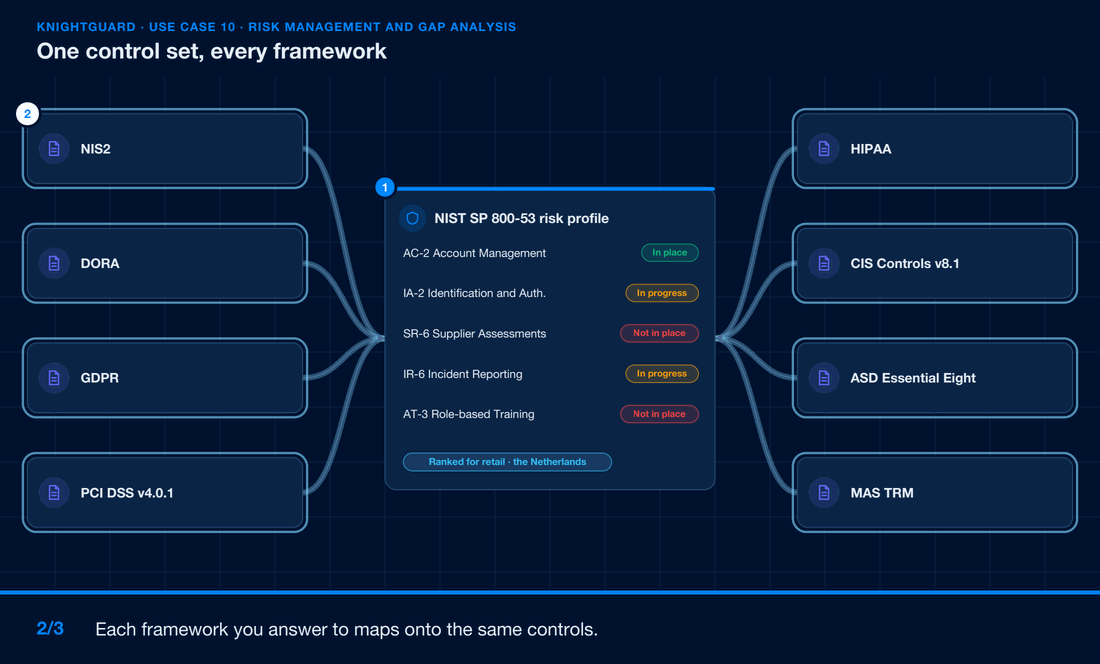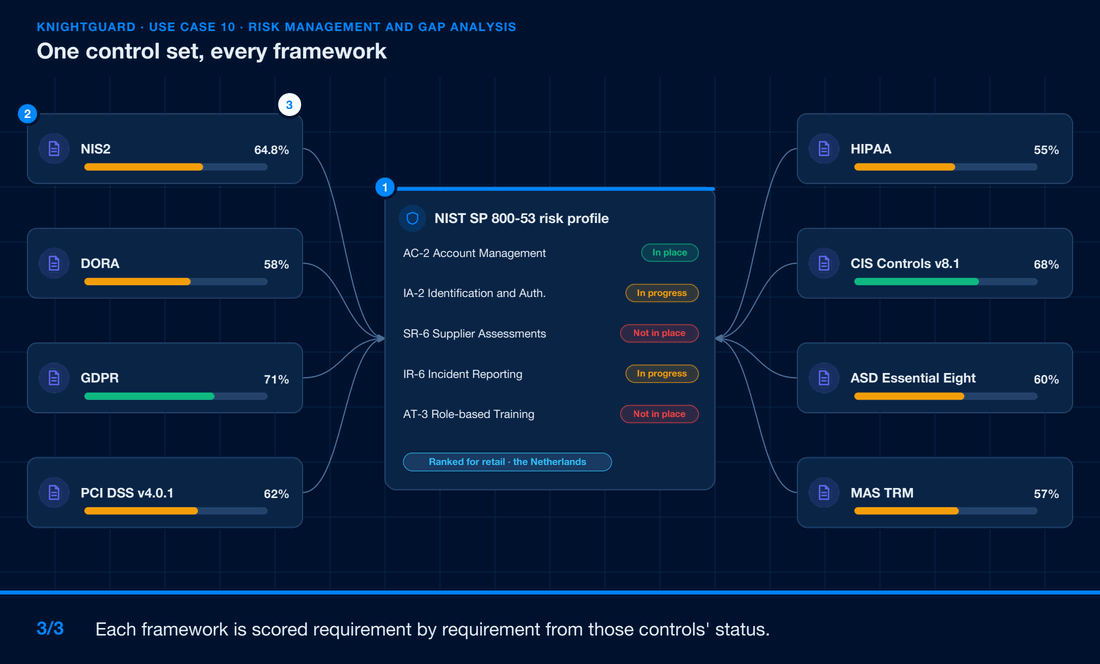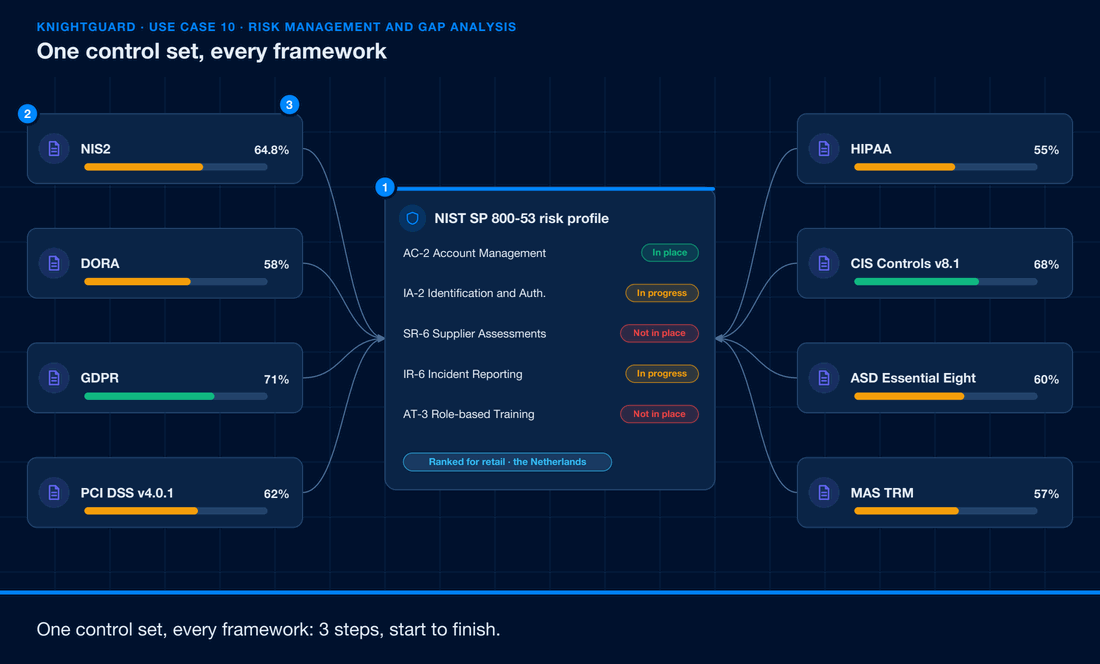
KnightGuard builds a risk profile on NIST SP 800-53, with controls ranked for your industry and region, and scores it against 22 compliance frameworks requirement by requirement. The top gaps are listed with the points each would add. A guided gap assessment combines a CTEM questionnaire with your technologies and scanner evidence, which outranks self-assessed answers, and ends in a 30/60/90-day roadmap.
Where it works in CTEM
Contribution by stage across the continuous exposure management lifecycle.
Share of this use case's platform capability at each CTEM stage. The five shares sum to 100%. & the cycle repeats continuously
SCOPING
30%Choose what you answer to. Start a risk profile from a framework, the NIST SP 800-53B baselines, your top ATT&CK techniques, ransomware (NIST IR 8374) or operational technology; controls are ranked for your sector and region.
DISCOVERY
15%Gather the evidence. The gap assessment records your technologies and services, imports scanner compliance reports, and reads internal compliance reports with your own AI provider, quoting what it finds.
PRIORITIZATION
30%Score and rank the gaps. Each framework scored requirement by requirement with a maturity band, and the top ten gaps listed with the requirements they affect and the points each would add.
VALIDATION
10%Evidence over opinion. Scanner evidence outranks questionnaire answers, maturity is capped unless a capability is continuous and unified, and answers carry evidence notes and attachments.
MOBILIZATION
15%Roadmap and reports. Owners and target dates per control, a 30/60/90-day roadmap with controls flagged for board attention, and the Framework Compliance and Gap Analysis reports as PDF.
How it works
Each step follows the CTEM stage it belongs to.
Choose a profile
Framework, 800-53 baseline or top techniques
Gather evidence
Technologies, scanner reports, internal reports
Weigh the evidence
Scanner outranks answers; maturity capped by criteria
Score and rank
Requirement scores, top gaps by score uplift
Plan and report
30/60/90-day roadmap, owners, PDF reports
Key capabilities
22 frameworks, one control set
NIS2, DORA, GDPR, PCI DSS v4.0.1, HIPAA, CIS Controls v8.1, ASD Essential Eight, SEBI CSCRF, RBI CSF, MAS TRM and more, all mapped to NIST SP 800-53, so one control counts everywhere it applies.
Ranked for your sector
Controls ranked by a top 100 for your industry and region. Profiles start from a framework, an 800-53B baseline (Low, Moderate, High), ATT&CK techniques, ransomware or operational technology.
Gaps with their uplift
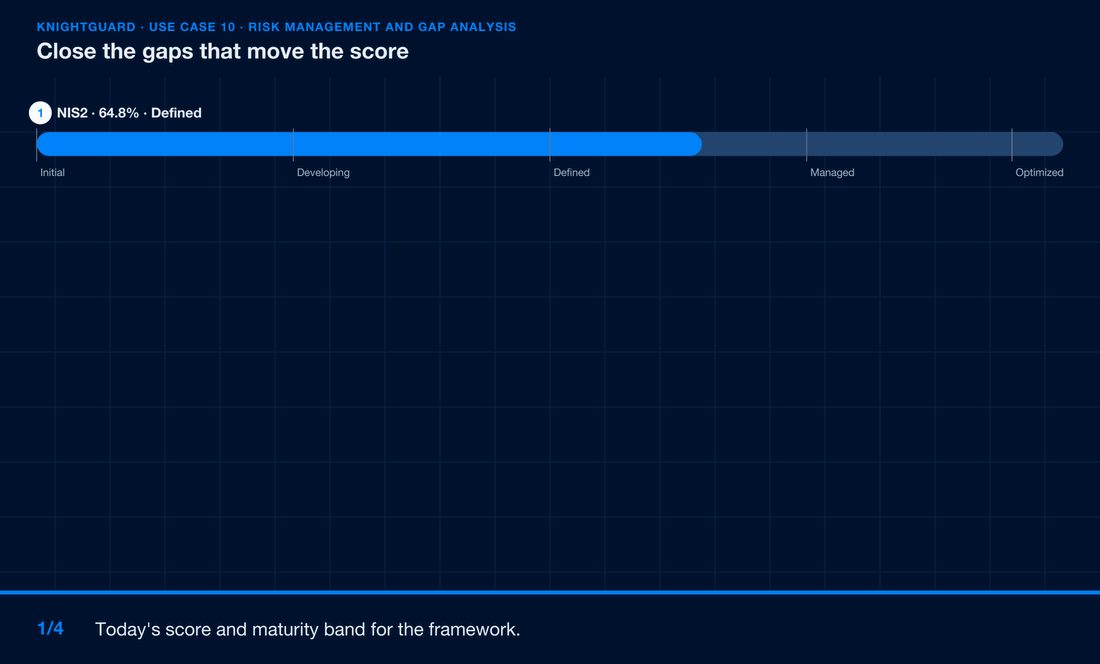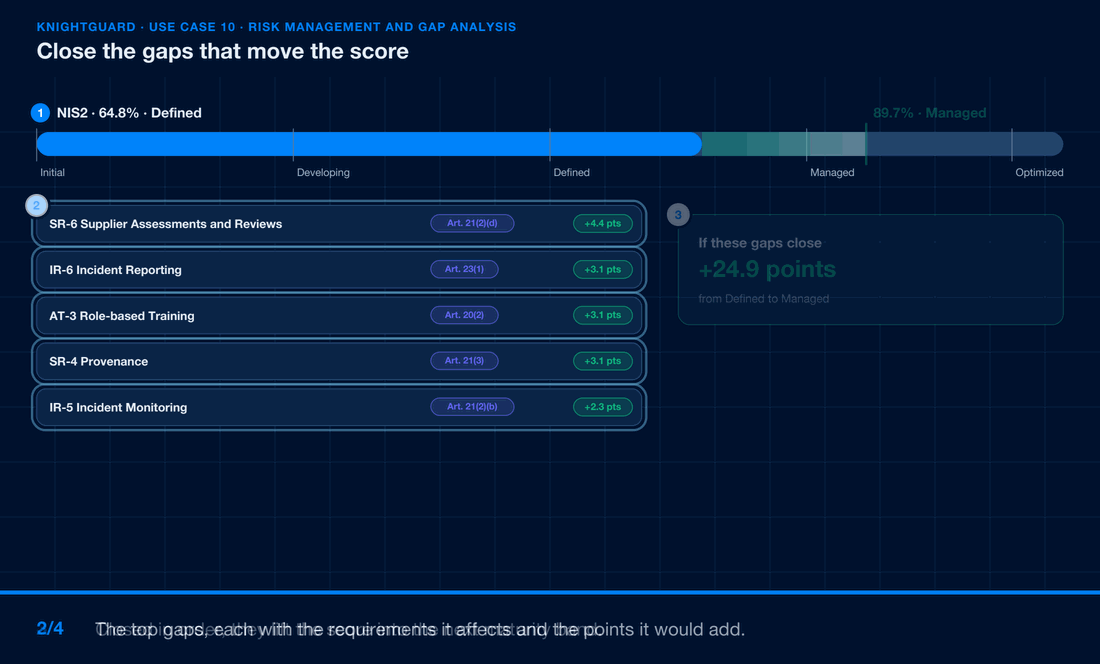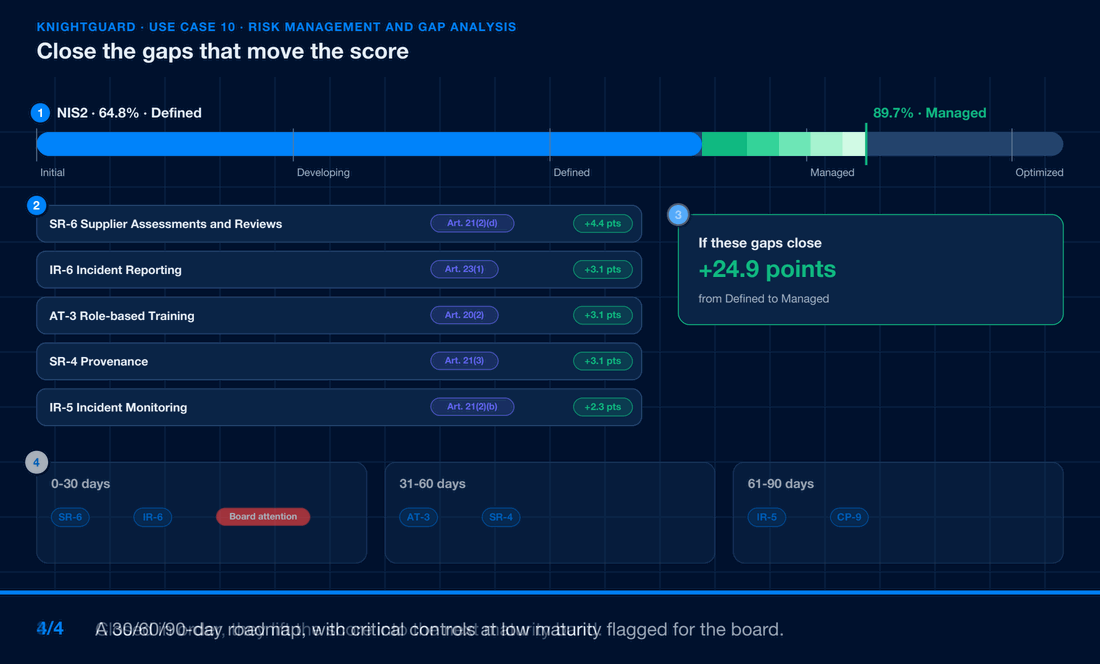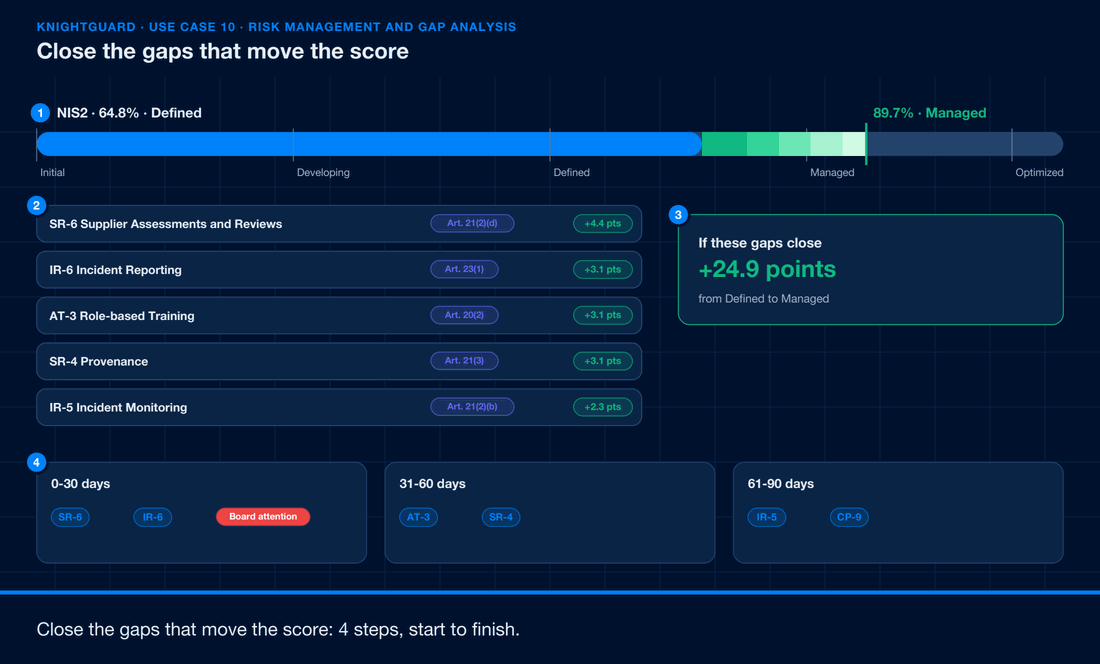
If these gaps close shows the score and maturity band you would reach; the top ten priority gaps list the requirements each affects and the points it would add.
Guided gap assessment
Seven steps and a questionnaire of core CTEM questions by stage plus the framework's own, each answered on a 0 to 5 maturity scale with a level guide and mapped through NIST CSF to 800-53.
CTEM programme posture
The assessment scores your exposure management programme stage by stage, from scoping to mobilization, alongside the framework, so process gaps show next to control gaps.
A plan the board can read
A roadmap in 0-30, 31-60 and 61-90 day waves, critical controls at low maturity flagged for board attention, and the CTEM Compliance and Gap Analysis reports as PDF.
One control set, every framework
One NIST SP 800-53 control set, ranked for your sector, scored against every framework you answer to.
Close the gaps that move the score
Today's score, the gaps that would move it most, the band they reach, and a 30/60/90-day plan.
Download the Risk Management and Gap Analysis Datasheet
Unlock the PDF linked to this use case after a short contact form. The file is saved to your downloads folder immediately after submit.
Ready to level up your cyber defence?
Supports modern enterprises with agentic AI discovery, real-time threat validation, and autonomous exposure prioritization.