Risk and Compliance
Measure what matters, reduce exposure, and build trust through security by design
Stages this advances
Highlighted stages are where this capability does the work.
Define the exposure surface that matters to the business.
Continuously inventory assets, identities and exposures.
Rank by exploitability and business impact, not CVSS alone.
Prove which exposures are actually exploitable.
Drive owners, SLAs and evidence to closure.
Scoping
Define the exposure surface that matters to the business.
Align crown-jewel systems, business services and third parties into scopes that executives recognise — not just IP ranges.
Prioritization
Rank by exploitability and business impact, not CVSS alone.
Threat intelligence, reachability and asset criticality collapse millions of findings into the few hundred that move risk.
Mobilization
Drive owners, SLAs and evidence to closure.
Automated routing into ITSM, owner accountability and board-ready evidence that exposure is trending down.
Structured Execution Workflow
End-to-end continuous exposure lifecycle mapping adversary actions into validated defensive posture.
01. Risk Profile
Gain insights into your Current Risk Profile and define your Target Risk Profile by systematically visualising your Security Program on Govern, Identify, Protect, Detect, Respond and Recover Functions. Go further deep and understand categories and subcategories relevant to your Risk Profile. Create multiple Risk Profiles based on departemnts, location, GRC compliance framework etc.
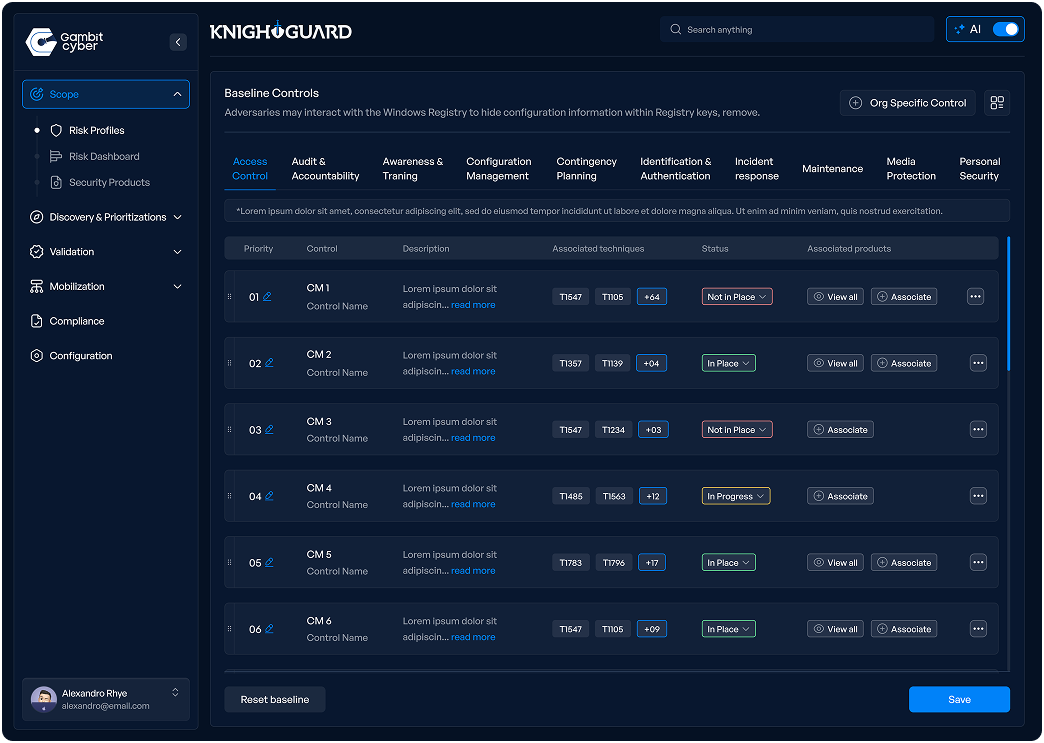
02. Controls Selection and Prioritization
Select security controls tailored to your organization's risk profile and compliance obligations. Prioritize controls based on your existing needs and risk apetite. Controls should span technical, administrative, and physical domains and align with industry standards and regulatory requirements.
03. Controls Implementation
Associate your Security Products with Compliance and Controls definition to gain AI-based Insights and Remediation Playbook on how to implement the policy, procedure or control specific to your environment and save hours in implementation. Gambit Cyber divides each subjective Control into a set of Actionable Tasks that can be tracked like a implementation step making it easier for your team to focus on a single actionable and measurable task. Integrate with any ticketing system of choice our use our inbuilt Ticketing System to track progress.
04. Audit and Reporting
Track and monitor all Audit and Reporting requirements from a single Consolidate Dashboard and feed it into your overall Effective Security Posture.
Download the CTEM Datasheet
Unlock the PDF linked to this use case after a short contact form. The file is saved to your downloads folder immediately after submit.
Related Capabilities
Adversarial Exposure Validation
See your Attack Surface the way an Attacker does, before they do
Threat Detection and Hunting
Find what others miss before it becomes a breach
Complete Attack Surface Management
Integrate Asset, Threat and Vulnerability data seamlessly to quickly identify critical Exposure Gaps