Adversarial Exposure Validation
See your Attack Surface the way an Attacker does, before they do
Stages this advances
Highlighted stages are where this capability does the work.
Define the exposure surface that matters to the business.
Continuously inventory assets, identities and exposures.
Rank by exploitability and business impact, not CVSS alone.
Prove which exposures are actually exploitable.
Drive owners, SLAs and evidence to closure.
Validation
Prove which exposures are actually exploitable.
Attack path analysis and safe simulation confirm whether a finding is reachable and whether controls stop it.
Mobilization
Drive owners, SLAs and evidence to closure.
Automated routing into ITSM, owner accountability and board-ready evidence that exposure is trending down.
Structured Execution Workflow
End-to-end continuous exposure lifecycle mapping adversary actions into validated defensive posture.
01. Threat Research, Prioritization and Profiling
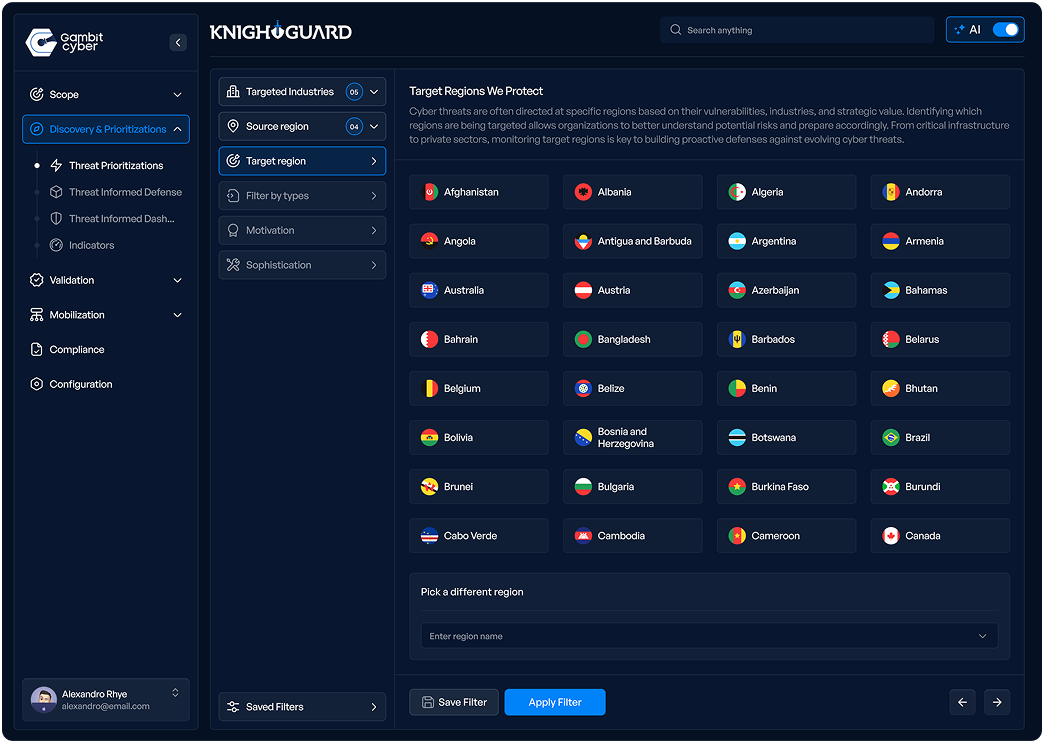
CTI Analysts find it difficult to unify, identify and prioritize threats across vaiorus Open and Closed Intel sources. Gambit Cyber’s KnightGuard Platform is Threat Intel agnostic, which means, organisations can easily integrate their own Threat Intel feeds and quickly gain a unified insights into the Threat Landscape. Our AI-enabled (fine tuned for a specific organisation) Threat Intel Ingestion pipeline helps organisations quickly convert any Threat Intel Report into actionable Threat Intel in minutes. Once all threats are ingested, quickly filter threats most relevant to you based on our comprehensive and intuitive Threat Filtering. In addition use our integrated single click GIR (General Intel Requirements) filtering to quickly zoom in on threats that matter most.
02. Monitor
While identifying and prioritizing threats is important, an equally important piece is monitoring for any behavioural changes in threats (for example: a new Technique is now being used by Black Basta). Threat Monitoring module in Gambit Cyber enables you to be on top of threats. Effective Threat Change Notifications provide per field level changes include old and new values so that you don’t spend time navigating what changed.
03. Emulate
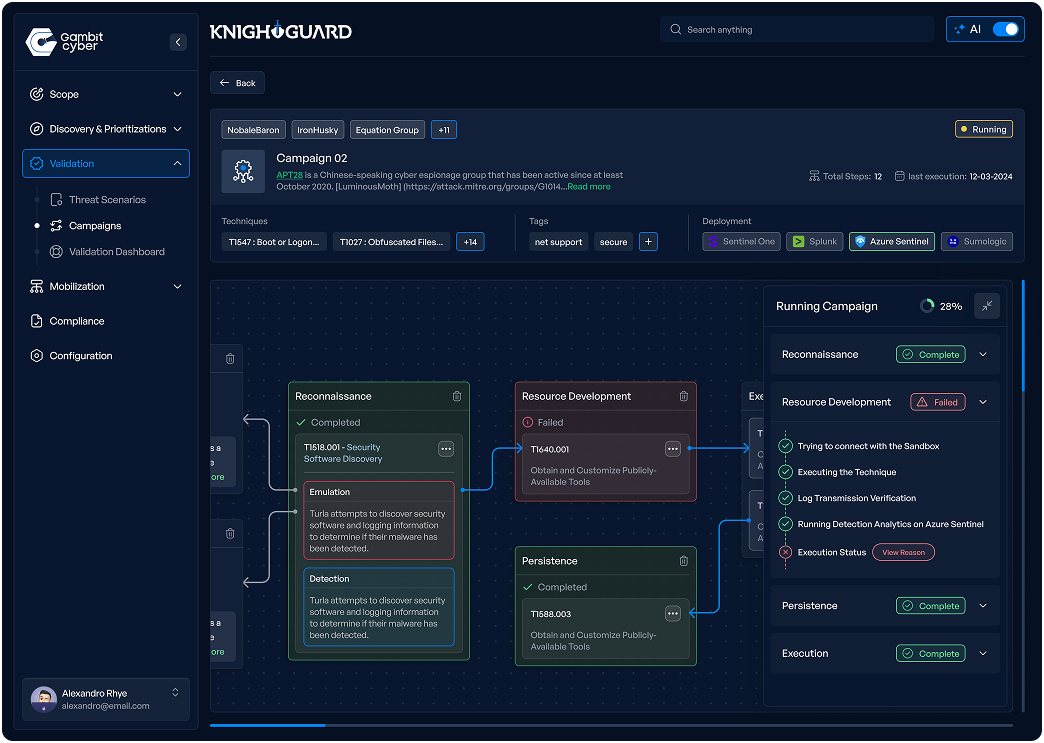
Once the relevant Threats have been identified, quickly generate Emulation Scenarios (aka Campaigns) to enable continous testing against latest Adversary behaviour. Emulation helps reveal how an attacker could chain tactics, techniques, vulnerabilities, weaknesses to reach your critical assets. We provide ready to emulate Threat Scenarios for hundereds of Attack Techniques. Our Red Team AI Agent can help you quickly generate emulation scripts helping you save hours of effort.
04. Detect
Quickly implement, test, validate and deploy Detection Analytics in any language and SIEM format right from the platform to quickly plug any gaps in your Security Controls. Use our Detection Analytics AI Agent to quickly generate Detections in any language format.
05. Measure
With a centralized Dashboard, gain insights into how well your Controls are working against Threats most relevant to your organisations. Map your Detection Analytics on to the MITRE Attack Frameowrk and visualise your Detection gaps and fix them quickly.
Download the Unified Exposure Validation Datasheet
Unlock the PDF linked to this use case after a short contact form. The file is saved to your downloads folder immediately after submit.
Related Capabilities
Threat Detection and Hunting
Find what others miss before it becomes a breach
Risk and Compliance
Measure what matters, reduce exposure, and build trust through security by design
Complete Attack Surface Management
Integrate Asset, Threat and Vulnerability data seamlessly to quickly identify critical Exposure Gaps