Threat-InformedThirdPartyRiskManagement
Download the Threat-Informed Third Party Risk Management Data Sheet to understand how KnightGuard helps you continuously monitor vendor exposure, identify adversary-driven attack paths, and build a robust, threat-informed third-party risk management program.
Download “Threat-Informed Third Party Risk Management”
Download the technical datasheet to get an architectural breakdown of capabilities, benefits, and implementation patterns.
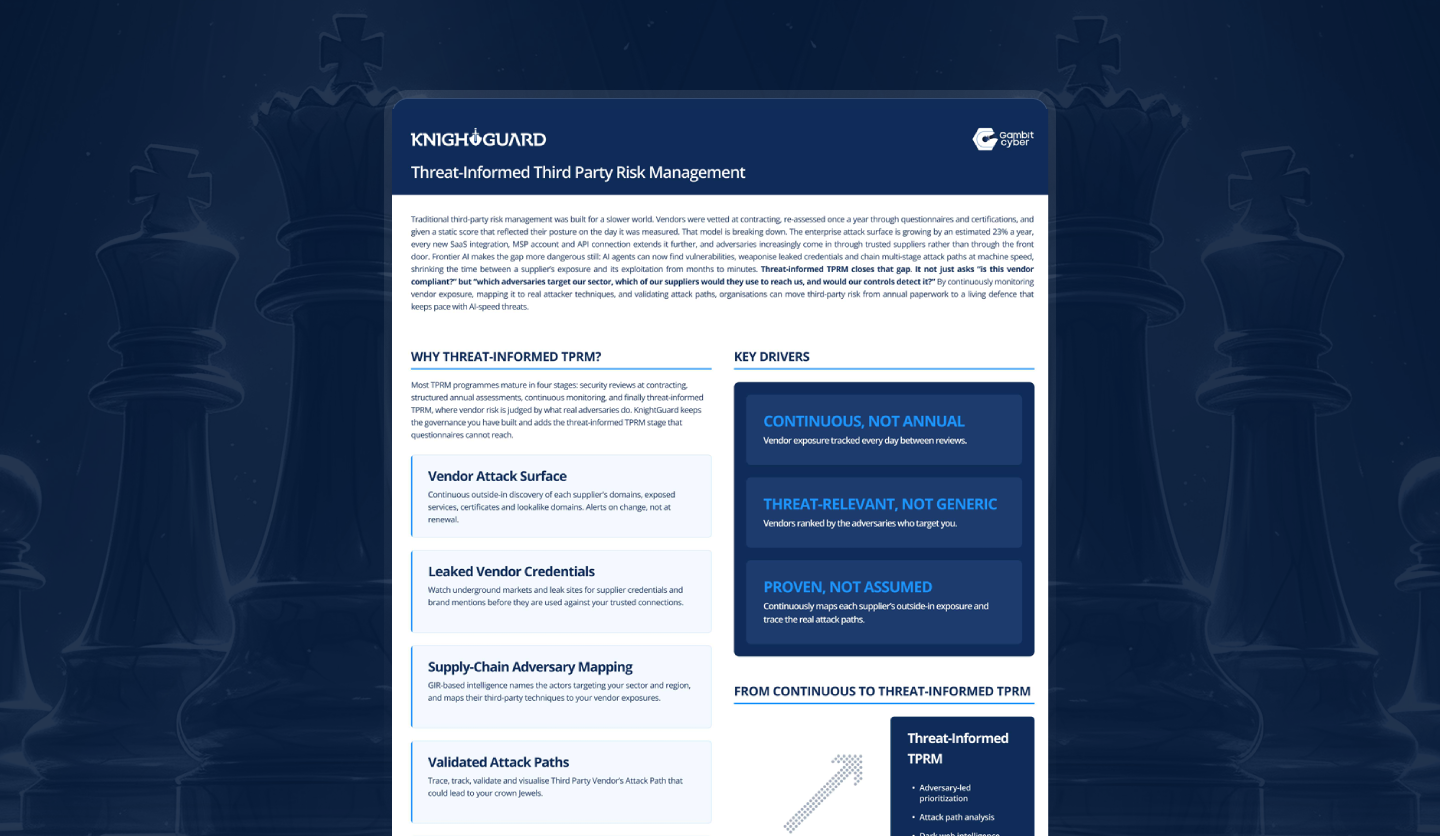
Knowing where your vendors are exposed is not enough. The critical question is: Which adversaries target your suppliers, how could they exploit those connections, and would your security controls detect the attack? KnightGuard Threat-Informed Third Party Risk Management (TPRM) answers these questions by continuously monitoring vendor attack surfaces, identifying leaked credentials, mapping sector-specific adversaries, and validating third-party attack paths. It transforms traditional annual vendor assessments into continuous, evidence-based risk management that keeps pace with evolving cyber threats.
Related Datasheets
Explore technical specs, architectures, and capabilities powering real-time exposure management.
Unified Vulnerability Management
Download the Unified Vulnerability Management Data sheet to understand how KnightGuard can help you build a robust, unified and continuous Vulnerability Management program.
Unified Exposure Validation
Download the Unified Exposure Validation Data sheet to understand how KnightGuard can help you build a robust and continuous Exposure Validation program.
CTEM Data Sheet
Download the CTEM Data sheet to understand how KnighGuard can help you build a robust and continuous Threat Exposure Management program.
Ready to level up your cyber defence?
Supports modern enterprises with agentic AI discovery, real-time threat validation, and autonomous exposure prioritization.